
Install with confidence
Reviewed definitions, pinned releases, and a known storage plan.
Install and manage trusted self-hosted apps while your Linux server and data stay yours.
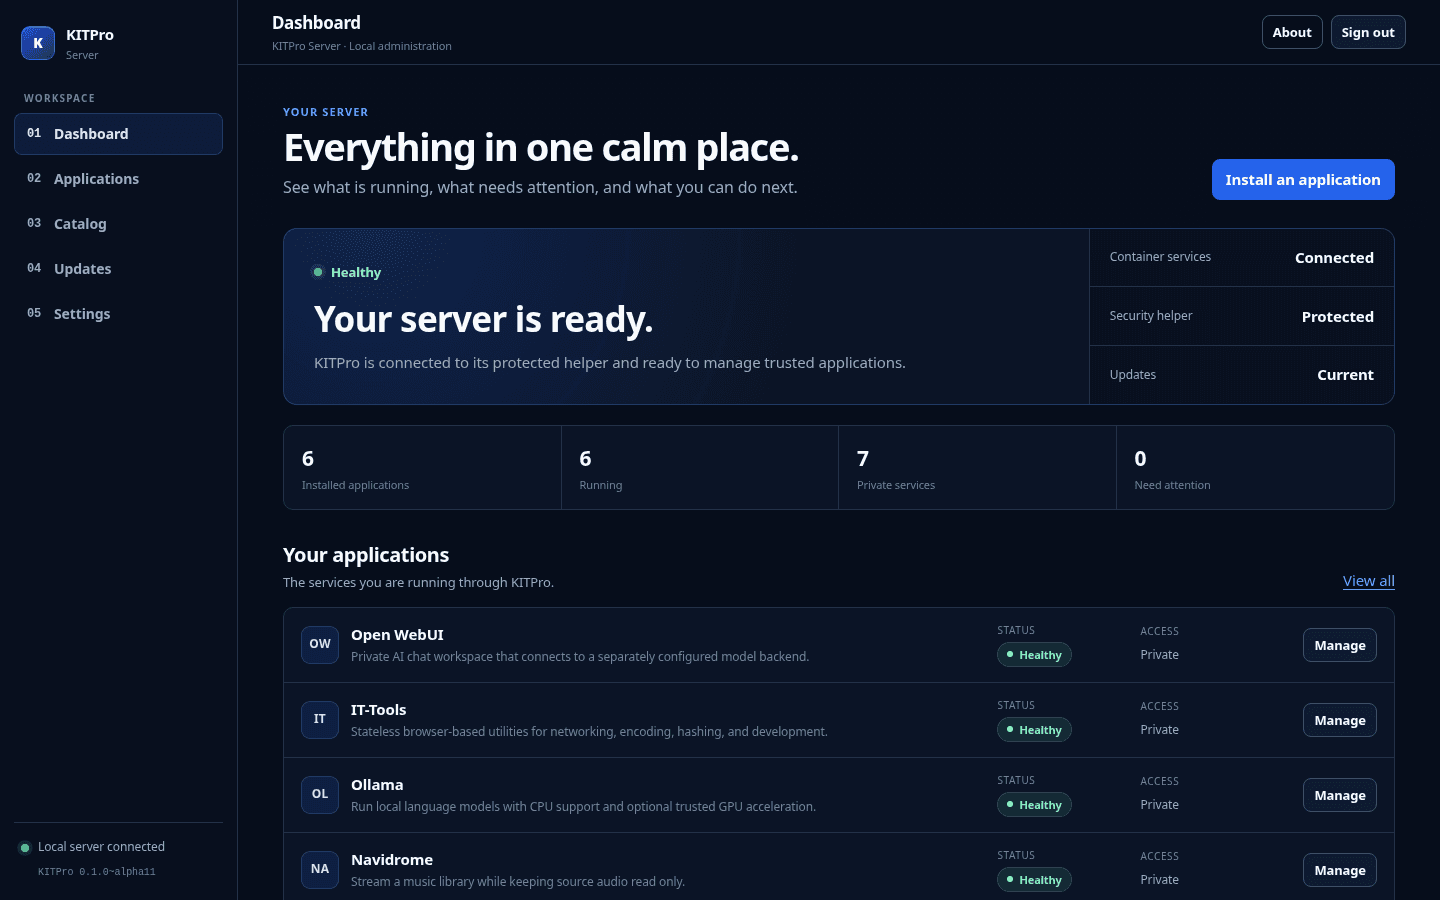
No cloud accountCore operation stays on your server.
Persistent dataApp storage survives runtime replacement.
Explicit accessYou decide exactly who can connect.
KITPro gives everyday server tasks a clear browser workflow. Standard Linux and Docker remain underneath, available when you need them.
Reviewed definitions, pinned releases, and a known storage plan.
Start, stop, recreate, and update without treating a container as storage.
No required KITPro cloud dependency stands between you and your apps.
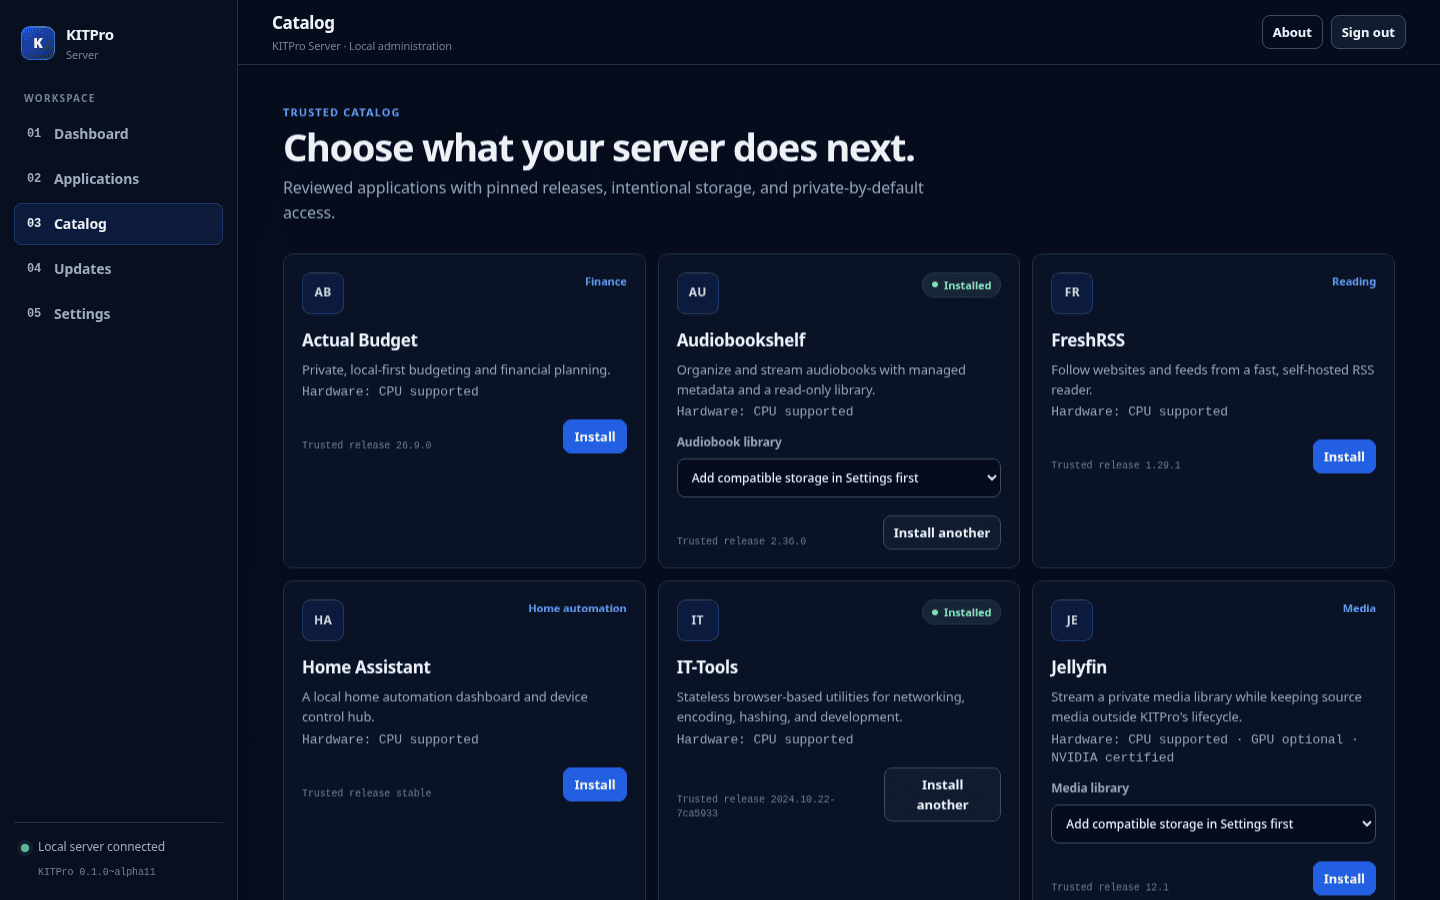
The catalog stays intentionally focused. Each app has a trusted definition, an intentional storage model, and private-by-default access.
Install, start, stop, recreate, and update from a browser. KITPro keeps the runtime replaceable while your installation identity and stored data stay stable.
See what needs attentionHealthy, stopped, and degraded states are easy to tell apart.
Open the exact endpointUse the address KITPro assigned after the application becomes ready.
Keep data outside the runtimeRecreation does not mean starting over.
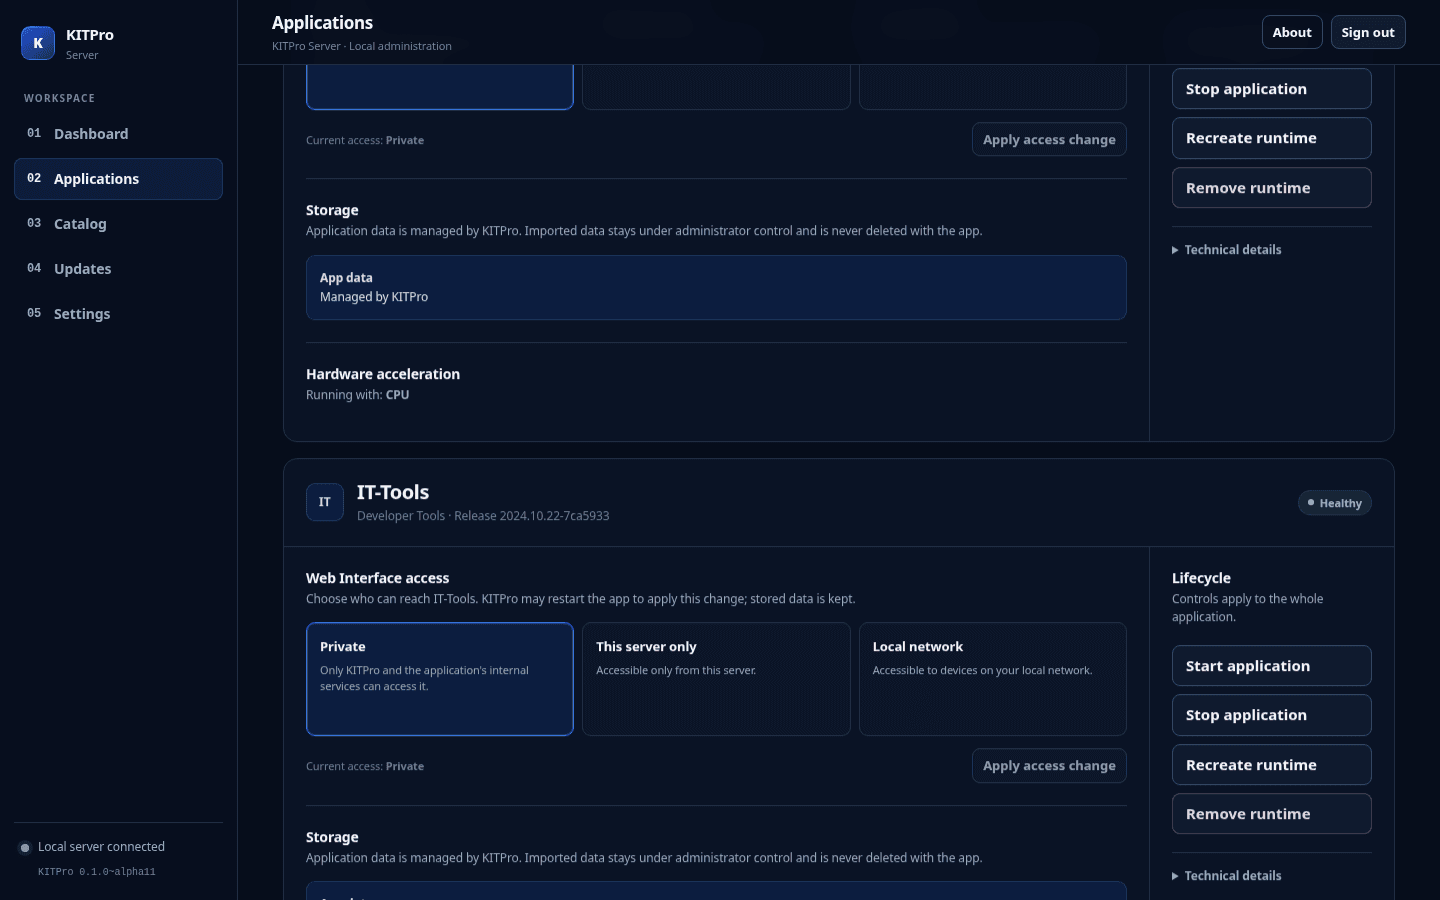
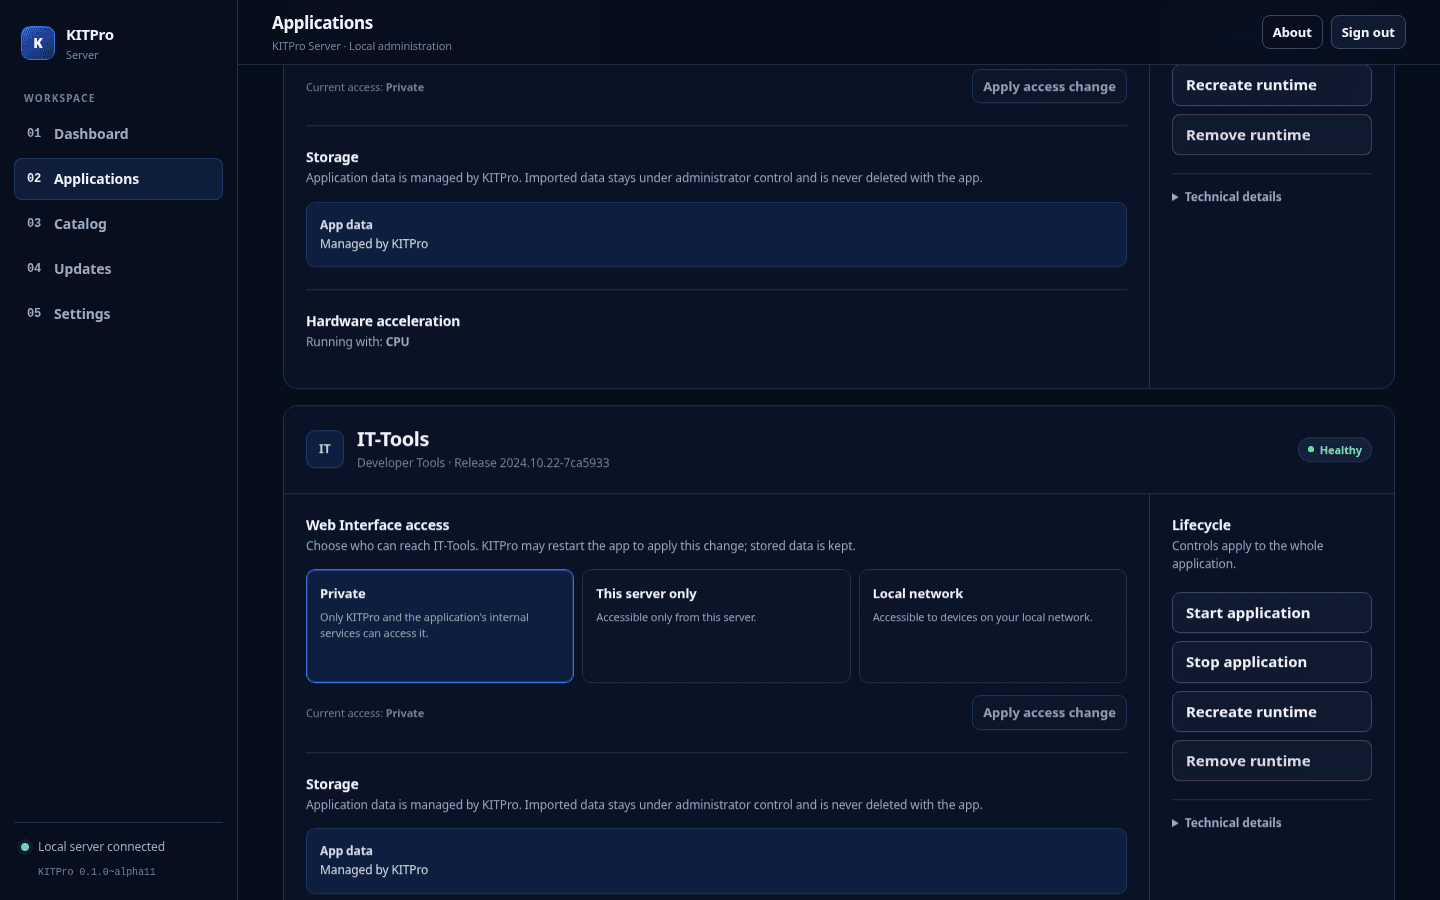
Pick the smallest useful audience for every application. Local network access is precise and is never treated as Internet exposure.
Only KITPro and the app's internal services can connect.
Use the app directly from the Linux host.
Share it at an exact address on your trusted LAN.
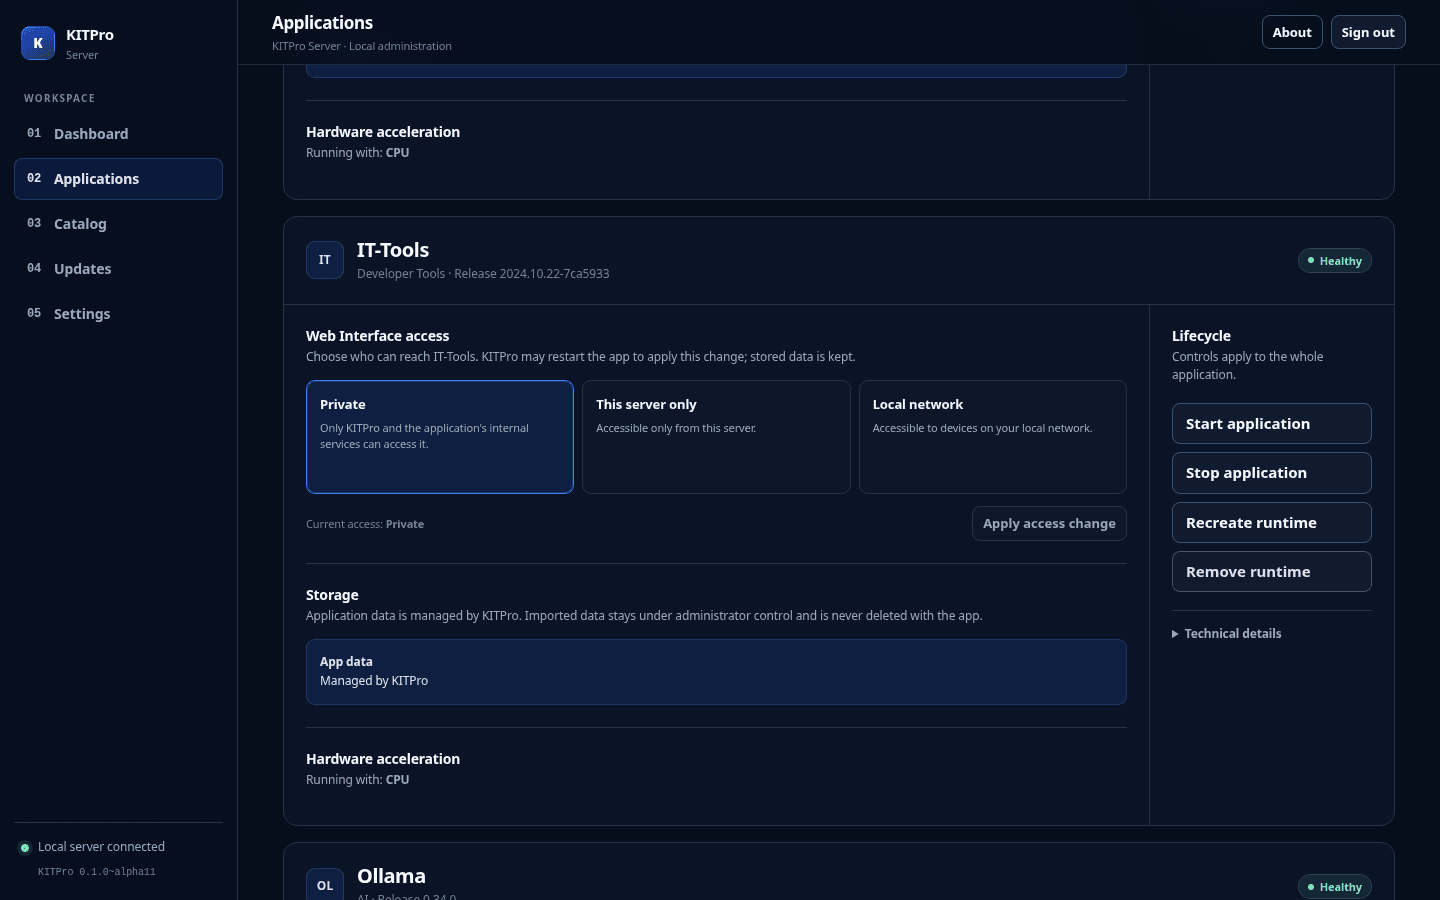
Recreating a runtime does not discard stored information. Removing a runtime and deleting its data remain separate choices.
Read the architecture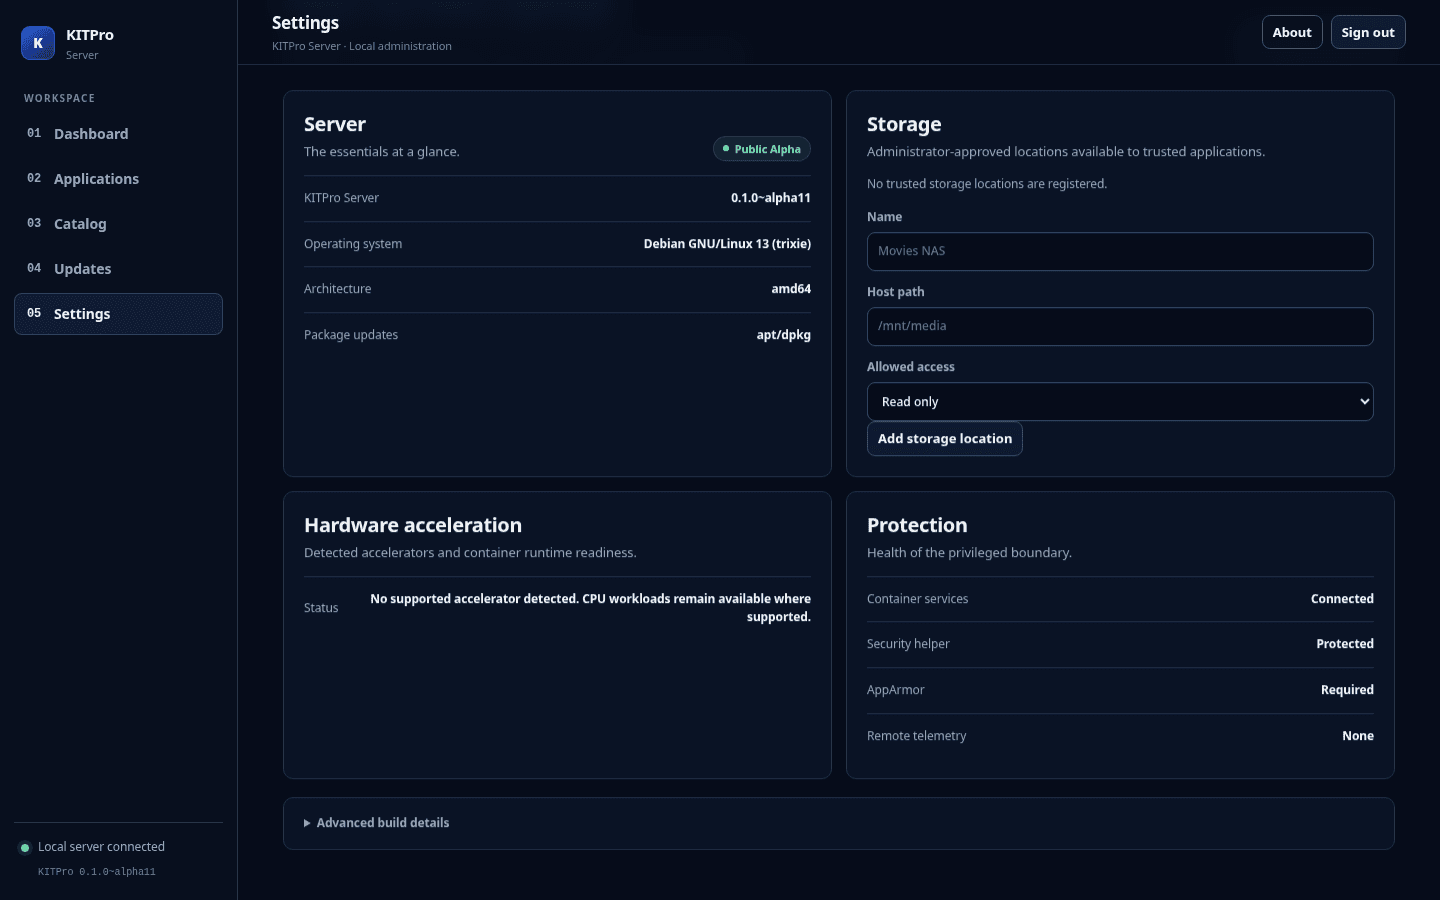
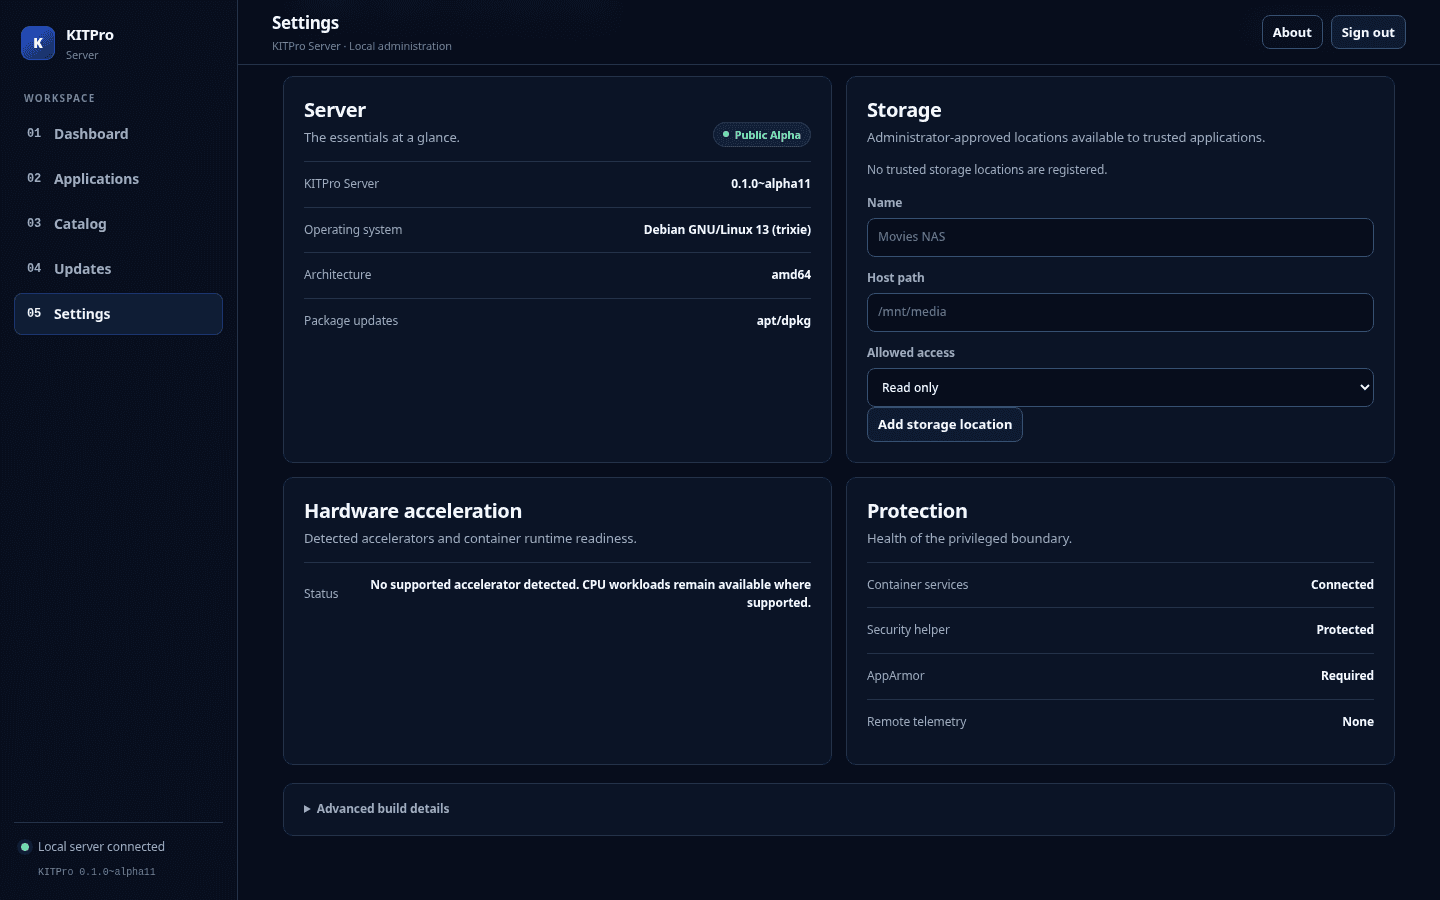
Jellyfin, Navidrome, and Audiobookshelf can read administrator-approved local or host-mounted NFS and CIFS libraries. SFTPGo receives one exclusive read-write location.
KITPro validates paths and mount identity instead of accepting raw Docker bind configuration.
Ollama supports CPU fallback and NVIDIA GPU acceleration. The public alpha is live-certified with an RTX A2000 12GB on Debian, Ubuntu, and Arch.
AMD, Intel, and Jellyfin transcoding are not yet certified.
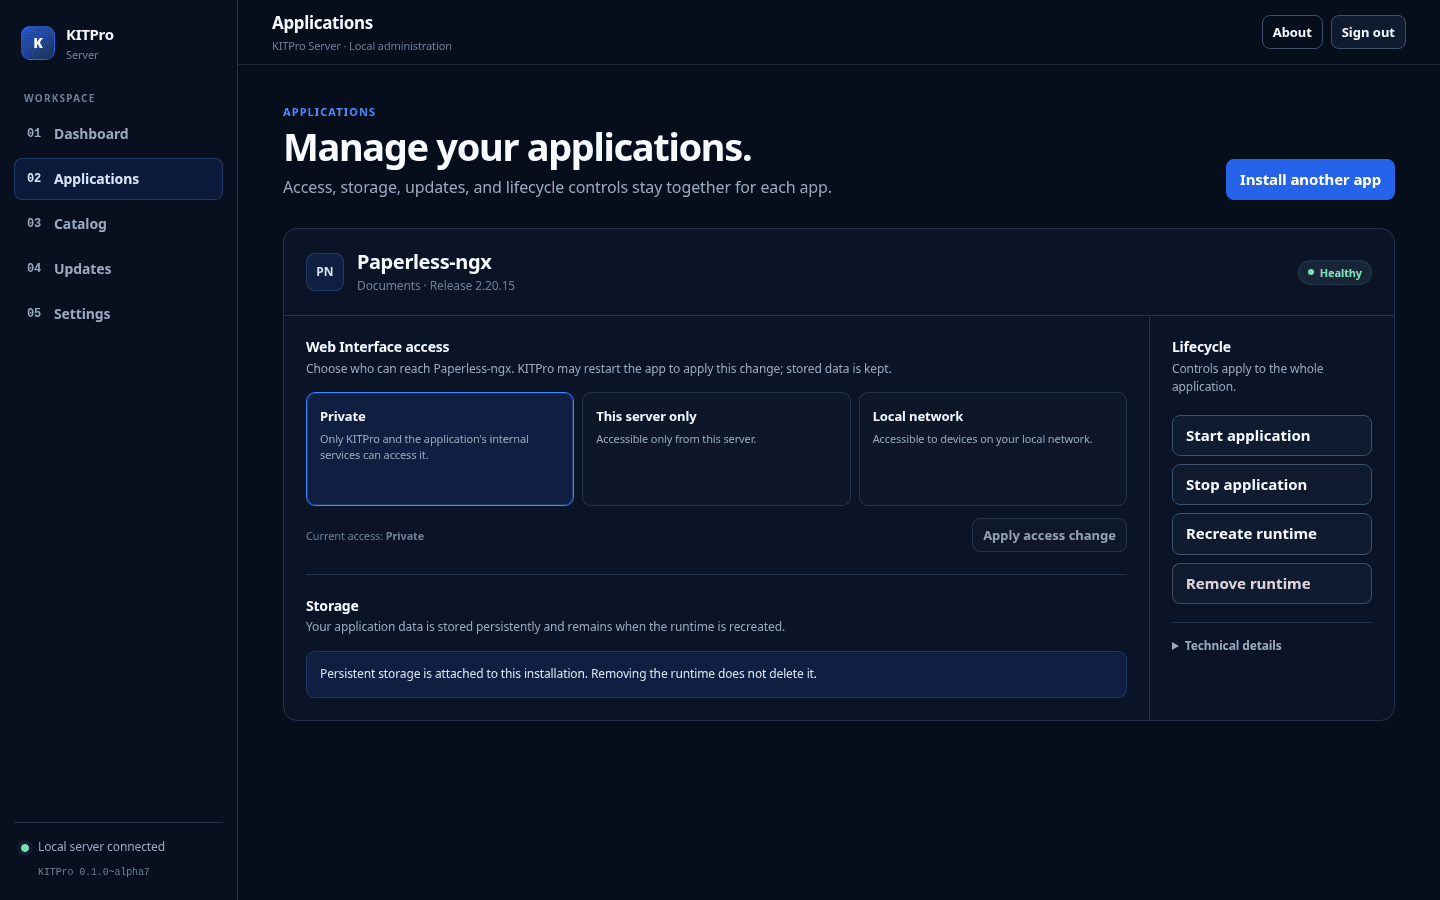
Paperless-ngx uses supporting services behind the scenes. KITPro manages the group together so it stays one application to install, expose, update, and recreate.
Native package updates and trusted catalog releases follow a bounded, observable flow. Nothing important is hidden behind a spinner.
Preflight the host and current state.
Protect control-plane state before migration.
Update through a bounded, visible operation.
Confirm health, storage, and access.
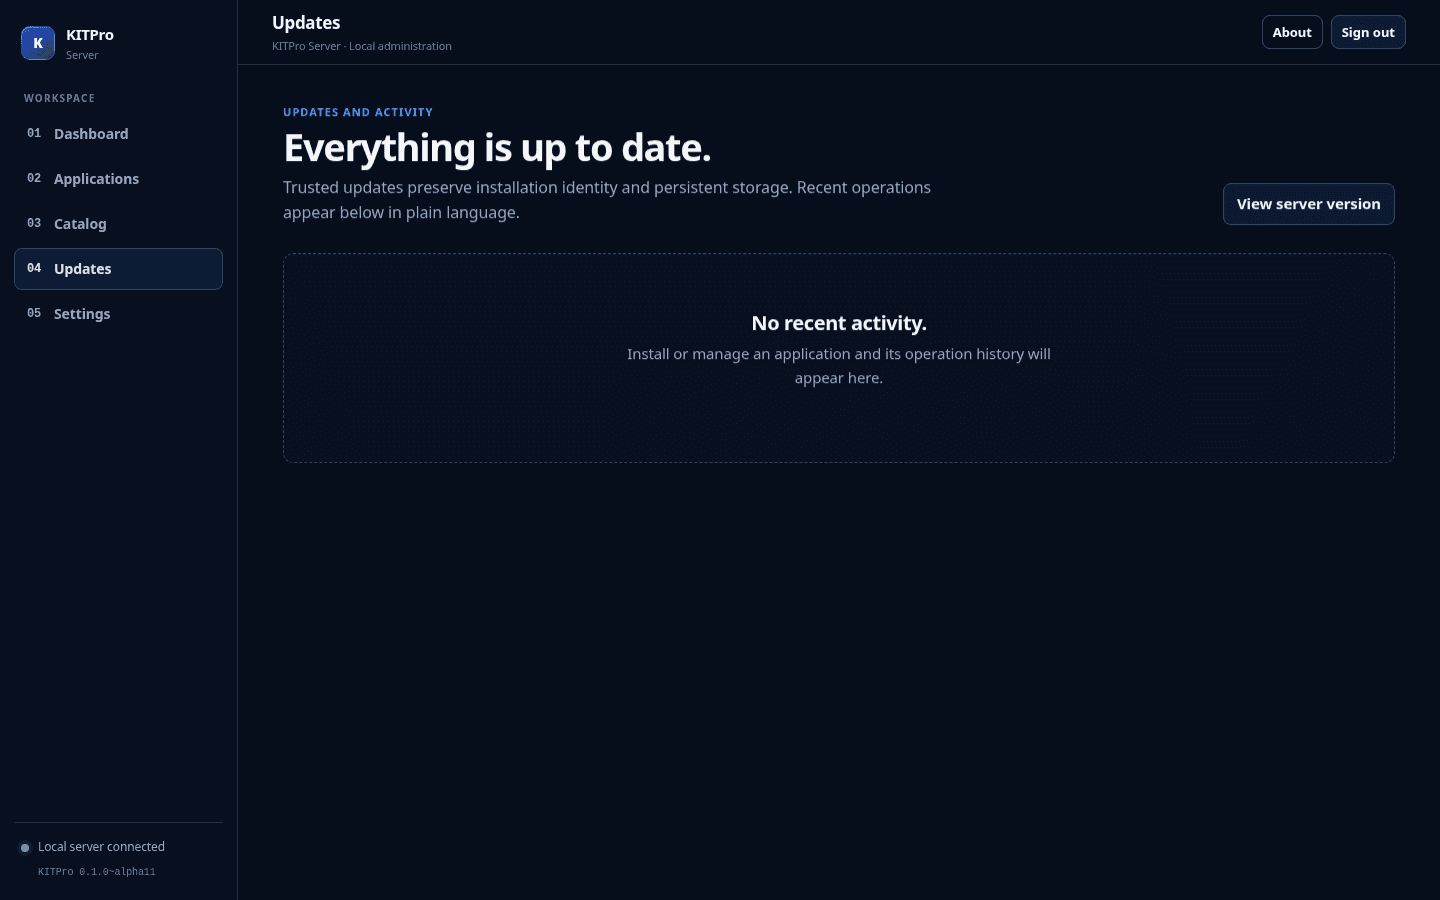
The web interface stays unprivileged. A confined helper independently validates approved operations before Docker changes occur.
Trusted definitionsNo arbitrary user-supplied Docker configuration.
Exact exposureWildcard publication is rejected.
Open sourceLicensed under Apache License 2.0.
Public alpha support focuses on well-understood, documented hosts.
The same control surface remains legible on mobile when you need to check health, review an operation, or open a trusted application.
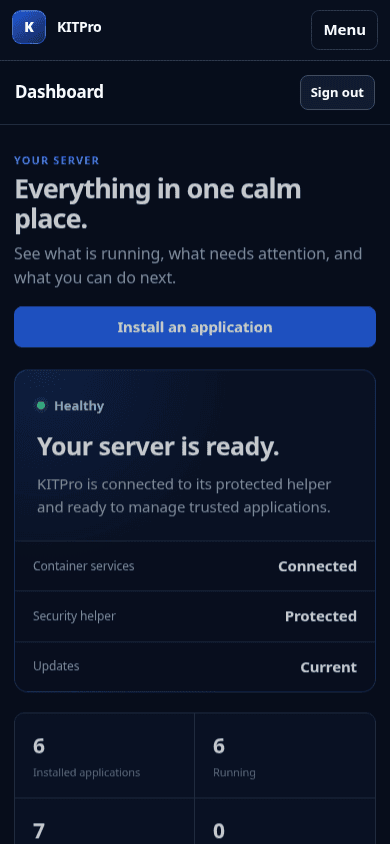
KITPro Server is ready for a careful first install.